Fintech
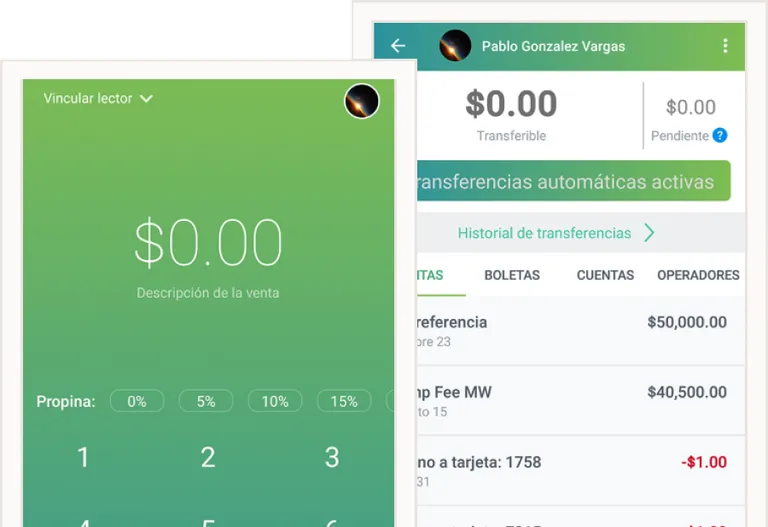
Sr. Pago
Native Swift and Kotlin apps with Bluetooth to an MPOS-type card reader, OneSignal and a transactional backend.
- Bluetooth
- MPOS reader
- OneSignal
- Notifications
- iOS+Android
- Native
PXL SECURITY
Hardening, pentesting, vulnerability management, compliance and incident response. For companies that have already had a recent scare.
What's included
Black-box, grey-box or white-box penetration testing of web and mobile applications, APIs and infrastructure. An executive and a technical report.
Static analysis of source code to detect vulnerabilities before production. Integrated into CI/CD.
Identification of CVEs in third-party libraries with a prioritised remediation plan.
Application of recognised security standards (CIS Benchmarks), granular identity and access management, network policies, secure credential handling and secure-by-default configuration.
Enterprise SSO, MFA, role management, just-in-time access and periodic privilege reviews.
A response plan, drills, runbooks and active support during a real incident when one happens.
Security integrated into the development cycle, continuous scanning, alerts and security posture dashboards.
Who it's for
We'll help you decide quickly. If we are not the right match, we point you to who is.
Problem
Companies treat security as a formality until they have an incident. That is when they discover the real cost is not the fine: it is the loss of market trust, the months of halted operation, the enterprise customers who cancel contracts and the investors who pause rounds. Treating security as optional or secondary is the most expensive technical decision any modern company makes.
Security breaches that expose customer data and trigger reputational crises
Regulatory fines for non-compliance with LFPDPPP, GDPR or HIPAA
Uninformed development teams writing vulnerabilities without knowing it
Misconfigured infrastructure with exposed secrets and excessive permissions
Improvised incident response that multiplies the damage
Outcomes
Security applied well does not only prevent incidents: it enables business opportunities. Companies with a mature security posture pass technical due diligence without friction, close enterprise contracts faster, raise capital at a better valuation and operate with the confidence of their stakeholders. A solid security programme is an asset, not a cost.
Reduced regulatory and financial risk from breaches
A DevSecOps culture with security integrated into the development cycle
Incident response rehearsed and documented
Demonstrable trust for investors, customers and partners
A security posture that is observable and continuously improvable
Process
Assessment of practices, existing controls, gaps against the target frameworks and prioritisation of initiatives.
A roadmap with low-cost quick wins, structural improvements and a path towards certification where it applies.
Hardening, automation, DevSecOps integration, training for the team and formalised policies.
Penetration testing after remediation. An executive and a technical report, and a plan for closing the findings.
Support alongside the external auditor for formal certification where it applies.
Monitoring, periodic scans, incident response exercises and updates to the controls.
Related case studies
Fintech
Native Swift and Kotlin apps with Bluetooth to an MPOS-type card reader, OneSignal and a transactional backend.
Fintech
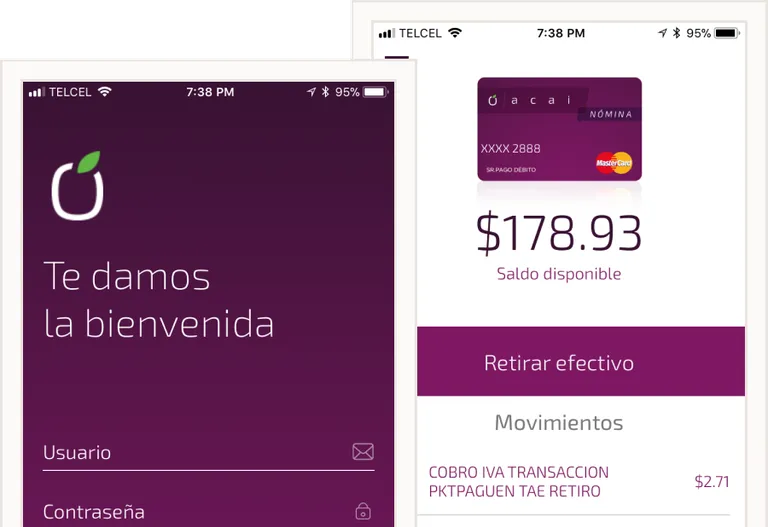
Complete payments platform with KYC, reconciliation and a real-time dashboard.
B2B SaaS
A RAG agent for 800+ employees with access to corporate documentation, procedures and operational data. Traceability and role control.
Stack | Tools | Standards
End-to-end security with industry and compliance tooling.
Frequently asked questions
It depends on the scope: a one-off pentest, a compliance review, incident response, or ongoing security. Reach out to us through Contact and we'll give you a clear quote based on what you need to protect.
Yes, you can hire just the pentest and receive the findings report. We also offer remediation support if you need it, but it's not mandatory.
Yes, we help implement technical controls aligned with these frameworks, including Mexico's Federal Law on Protection of Personal Data Held by Private Parties (LFPDPPP) for companies operating in Mexico.
Yes, we offer security incident response.
Yes, Vanta and Drata are among the tools we use in PXL Security to automate compliance evidence collection.
Related services
PXL AUDIT TECHNICAL
PXL Audit Technical
Technical audit. An honest picture of the real state of your code, architecture and infrastructure.
PXL CLOUD
PXL Cloud
Cloud architecture. Infrastructure that scales with you, not against you. AWS, GCP and Azure.
PXL DEVOPS
PXL DevOps
CI/CD and continuous delivery. Deployments without fear, live observability and SRE practice for serious teams.
A 30-minute call about your current posture. The initial diagnosis is free.